
Secure a Copilot rollout
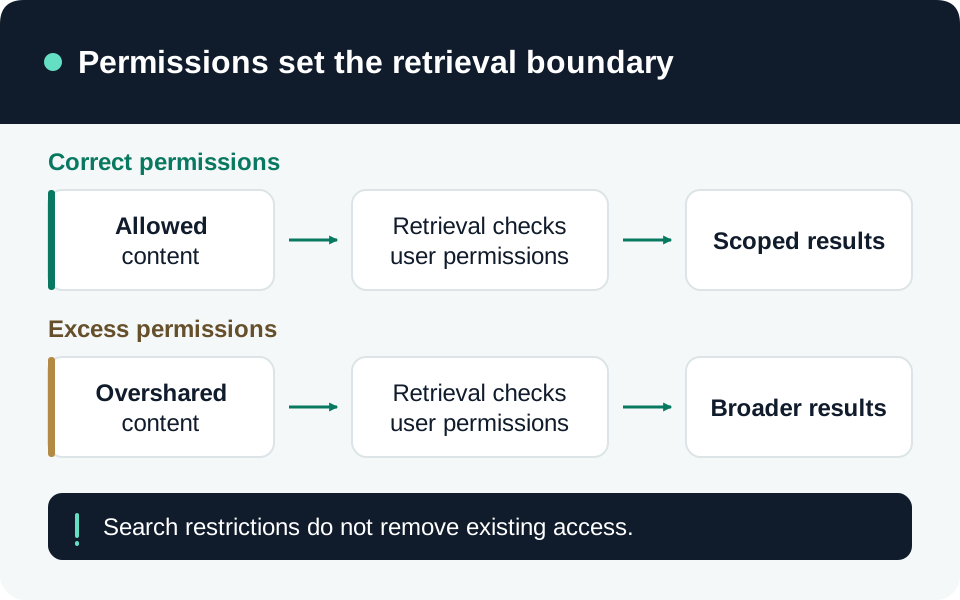
Move from an access inventory to scoped permissions, protected content and usable investigation evidence.
Microsoft 365 administrators
Explore this path →A clear route through the library
7 practical reading paths, organized around the work you own. Each step ends with a concrete outcome to record.
Move from an access inventory to scoped permissions, protected content and usable investigation evidence.
Microsoft 365 administrators
Explore this path →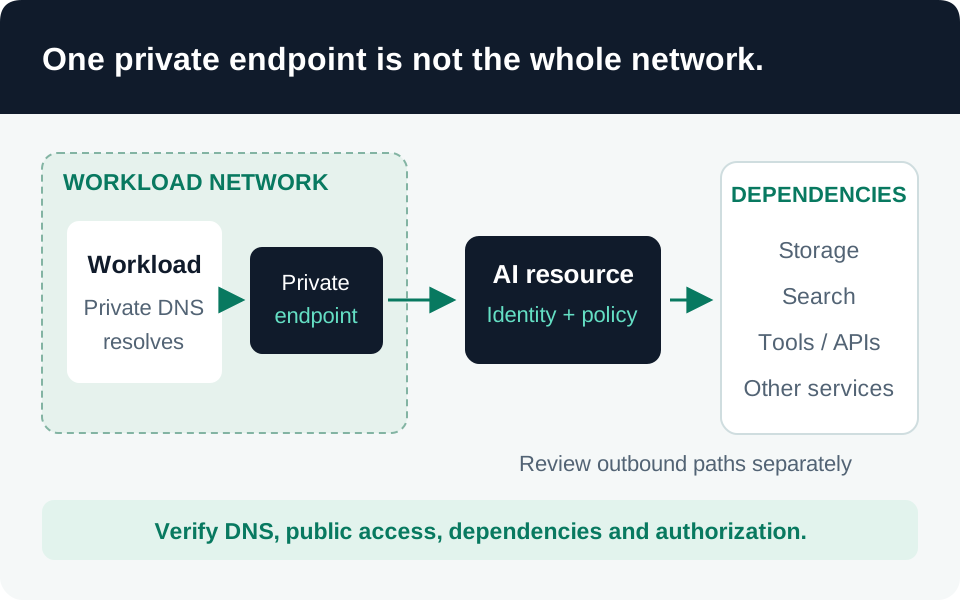
Design explicit identity and network boundaries, test untrusted input, and make a release decision with evidence.
Cloud engineers & application teams
Explore this path →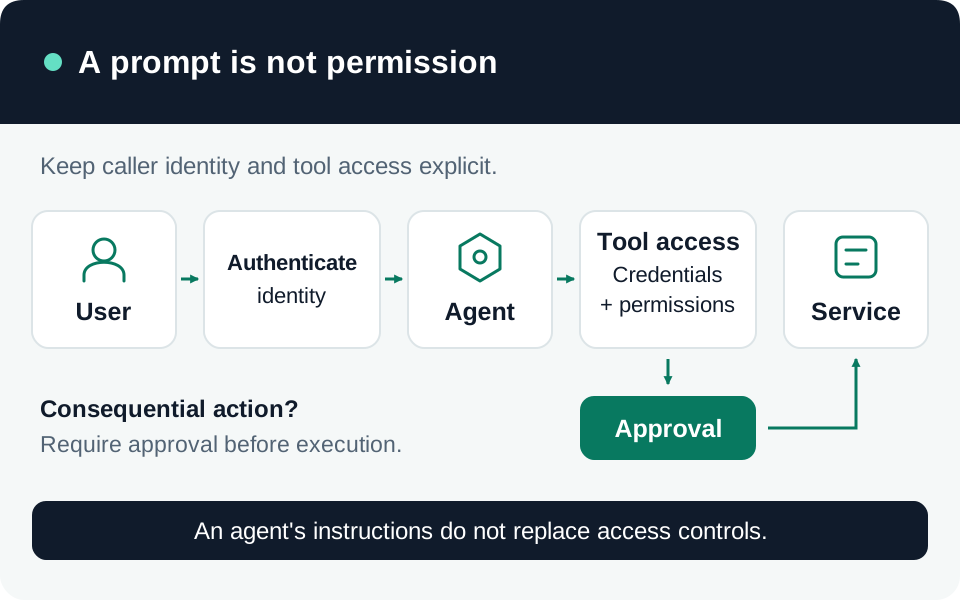
Understand who a tool acts as, constrain its destinations, and require meaningful approval for consequential actions.
Agent builders & platform owners
Explore this path →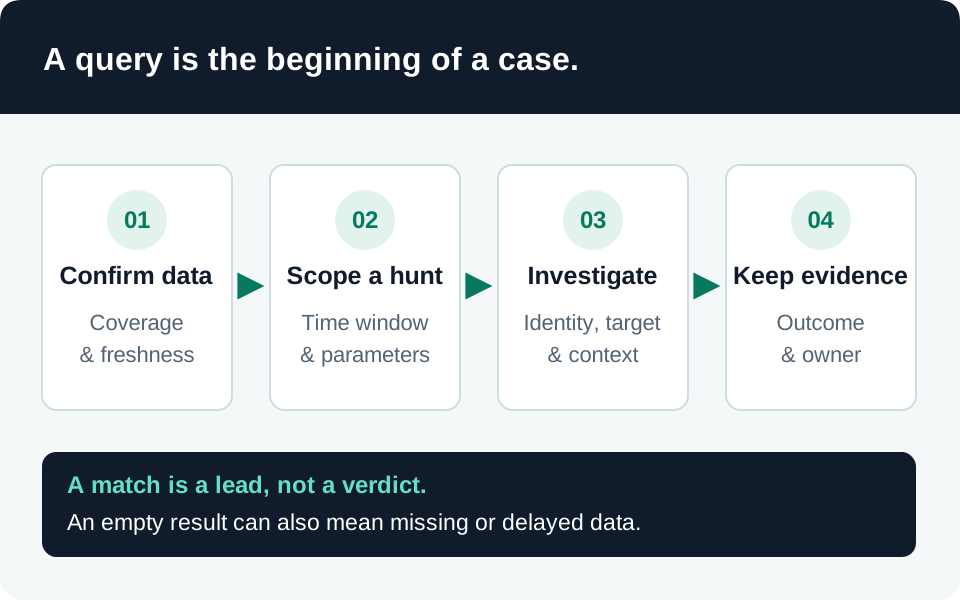
Start with data coverage, hunt identity and control-plane changes, and build a response around evidence.
SOC analysts & detection engineers
Explore this path →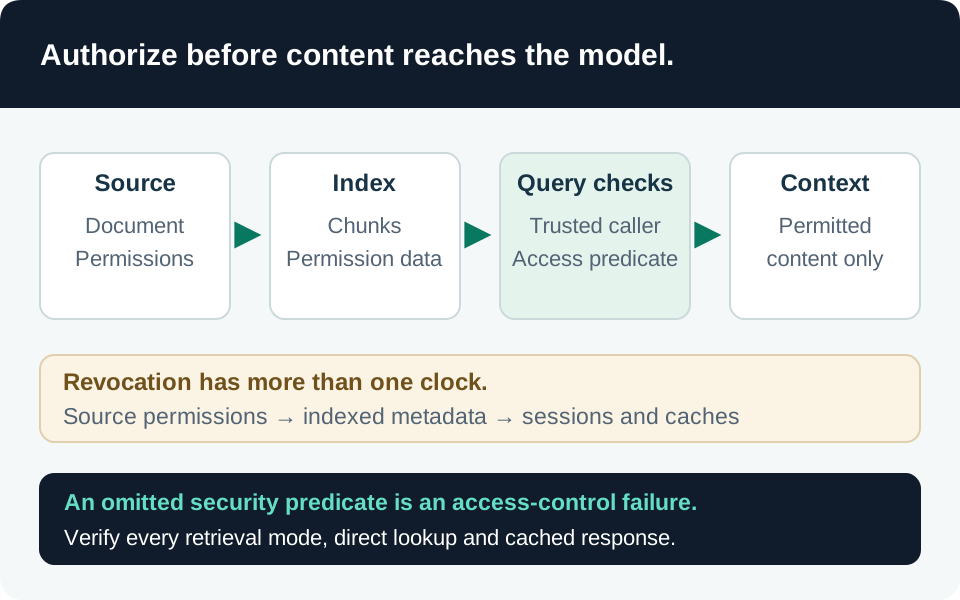
Follow document authority through ingestion, retrieval, caching and operational evidence.
Search engineers & AI architects
Explore this path →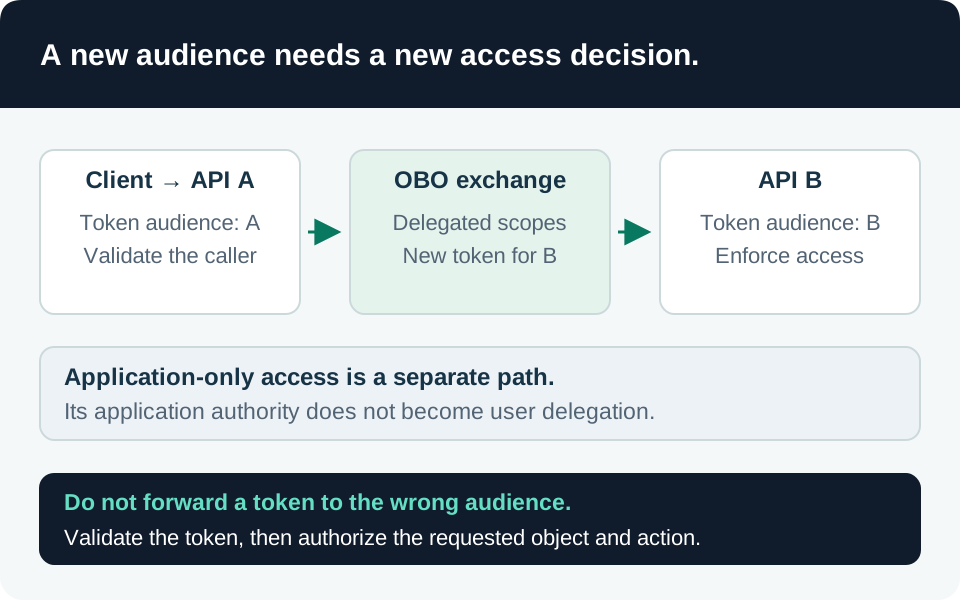
Separate federation trust, user delegation and application authority, then correlate changes with sign-ins.
Identity engineers & SOC analysts
Explore this path →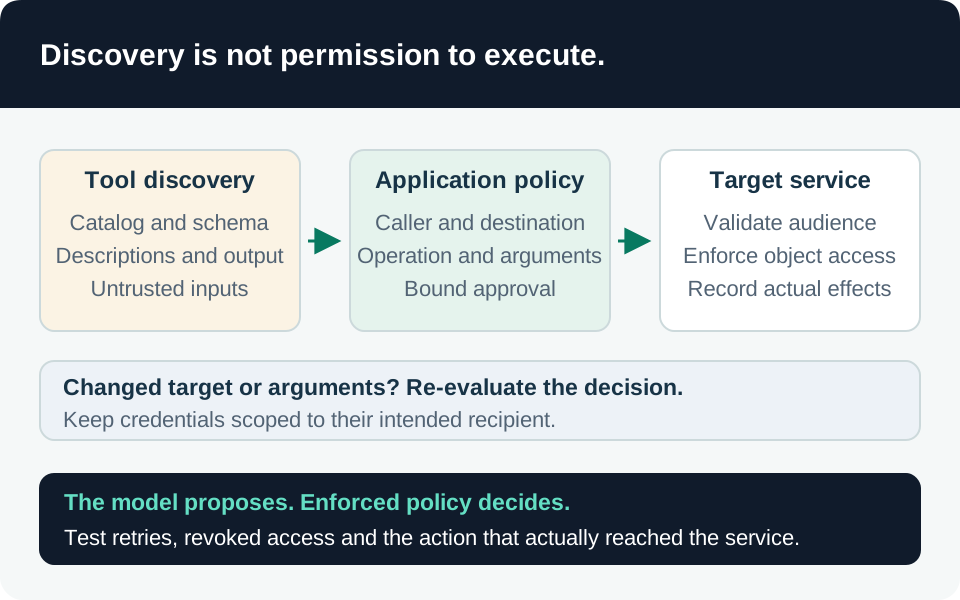
Review tool authority, gateway enforcement, adversarial experiments and detection evidence together.
Agent builders & security evaluators
Explore this path →Reading a guide does not verify a deployment. Keep the artifacts and test results from each step, record gaps, and make a release or escalation decision with the accountable owner.