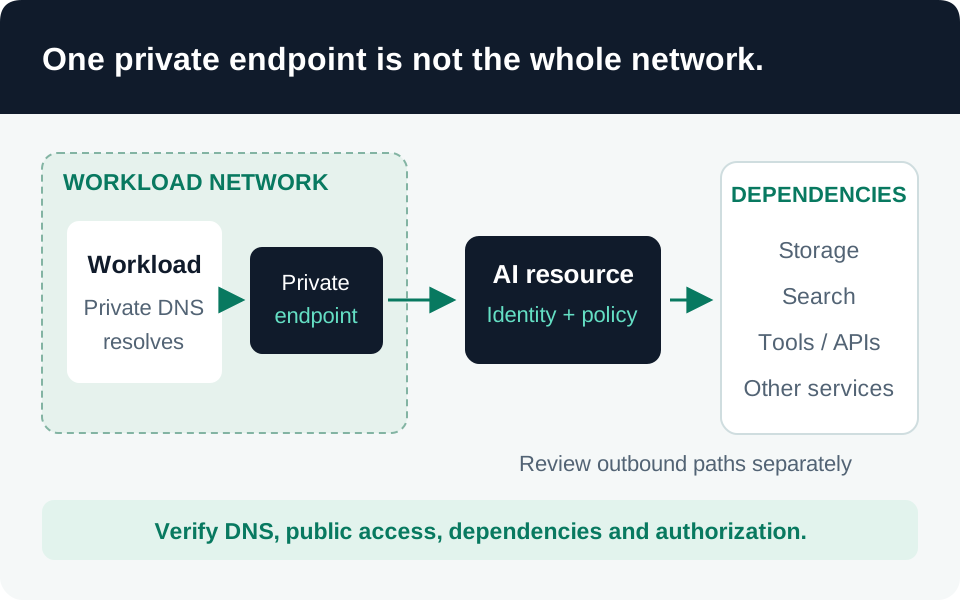
Control AI egress and private DNS across network boundaries
Trace inbound access, agent outbound traffic, hybrid DNS, and external tool destinations as independent controls, then test failure and recovery paths.
Explore the topic
Verify endpoint scope, DNS resolution, outbound dependencies and fallback paths in the actual execution environment.
Questions this collection helps you answer
Build your understanding
Trace inbound access, agent outbound traffic, hybrid DNS, and external tool destinations as independent controls, then test failure and recovery paths.
Separate caller authorization, backend identity, semantic-cache isolation, token budgets and private connectivity in Azure API Management.
Separate private inbound access, DNS, outbound dependencies, and identity checks before calling a Foundry deployment network-isolated.
Move from control to evidence
Use these as investigation leads. Table coverage and context determine what the results can establish.
Find recorded Microsoft.CognitiveServices write operations and distinguish configuration activity from model inference.
Inventory successful storage-account and private-endpoint connection mutations, then compare configuration evidence before claiming that network access was widened.
Identify Activity Log failures containing authorization or forbidden outcomes while acknowledging requests rejected before operation start are absent from this source.
Follow the connections