Agents4 min read
Govern agent connectors before they move data
Turn a Copilot Studio connector inventory into scoped data policies, verified endpoint controls, and accountable changes across environments.
Documentation checked
Explore the topic
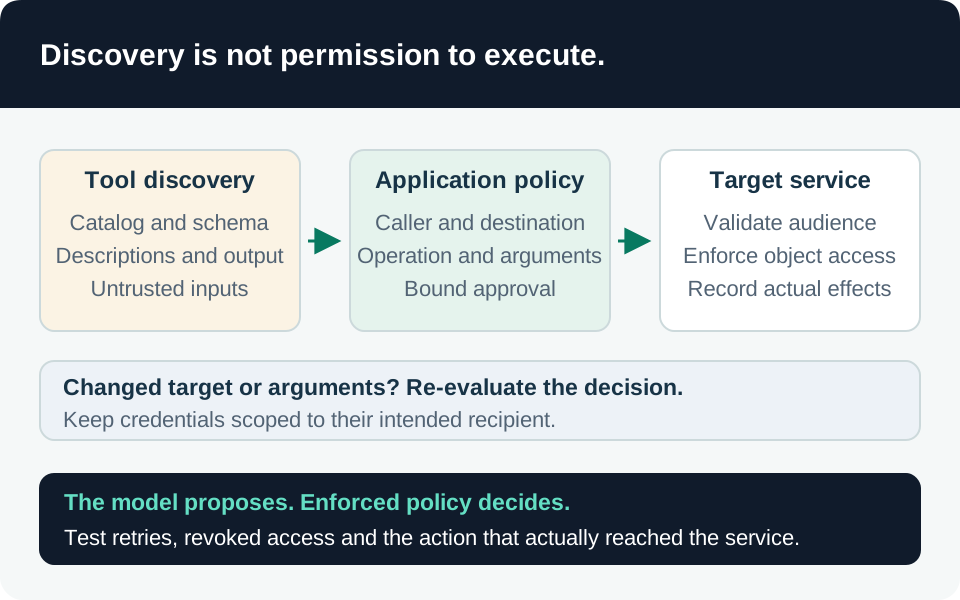
Separate tool discovery, transport authentication, token audiences and backend authorization.
Questions this collection helps you answer
Build your understanding
Turn a Copilot Studio connector inventory into scoped data policies, verified endpoint controls, and accountable changes across environments.
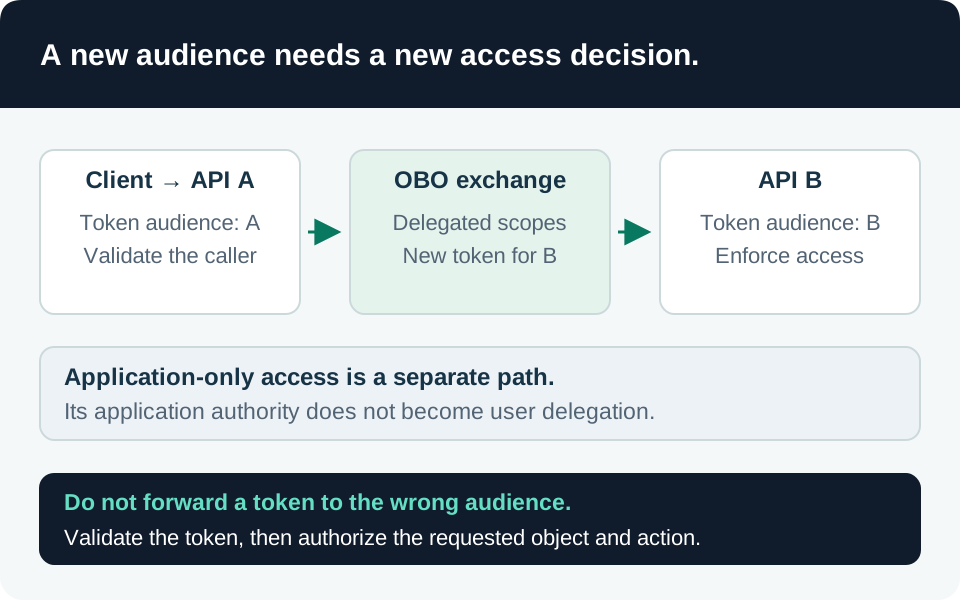
Separate user delegation from application authority, validate token boundaries, and prevent an agent from turning an authorized session into an unauthorized action.
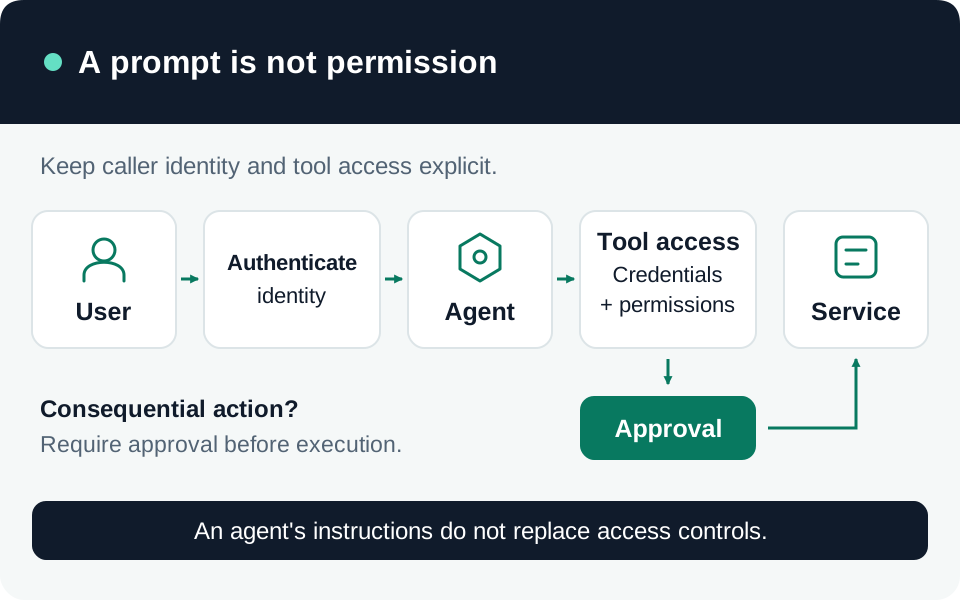
Design per-request authorization, tool admission, downstream identity and consequential-action approval for remote MCP integrations with Microsoft Foundry.
Move from control to evidence
Use these as investigation leads. Table coverage and context determine what the results can establish.
Compare successful workload resource identifiers against a prior baseline without treating token issuance as proof of new permissions or data access.
Preserve initiator identity and every target's permission-change evidence for successful app-role, delegated-permission and consent events.
Follow the connections