Governance5 min read
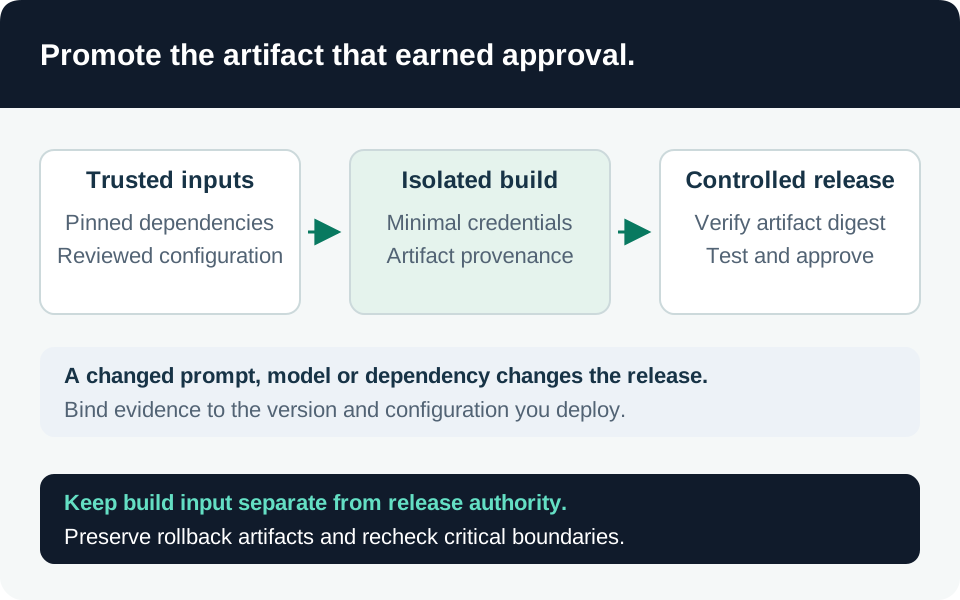
Advanced guideVersion the model-facing release as a complete manifest, verify artifact identity and provenance, isolate deployment authority, and rehearse rollback without trusting mutable tags.
Documentation checked↗
Identity & authorization7 min read
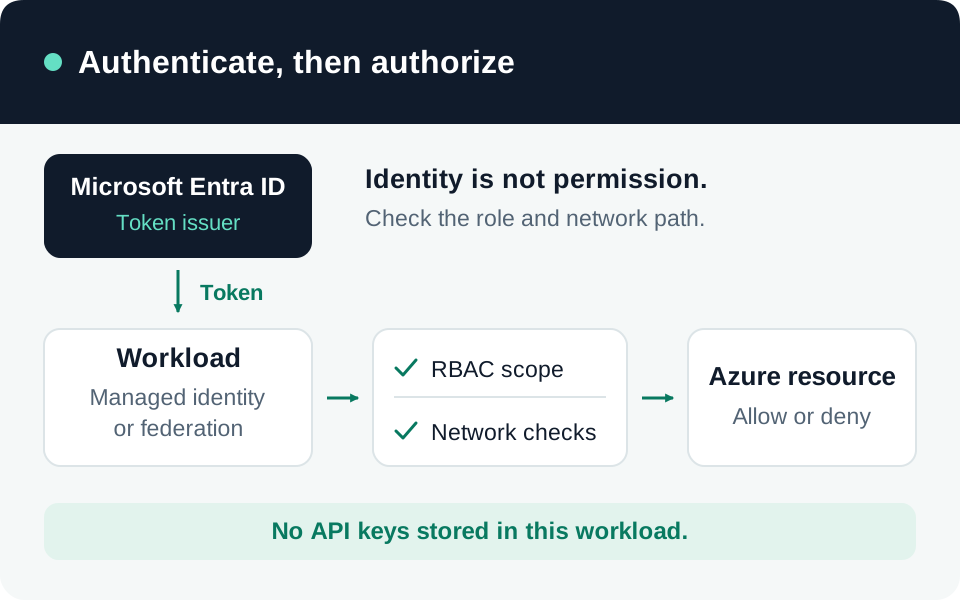
Advanced guideDesign issuer, subject, audience, and resource-permission boundaries so secretless deployment and runtime identities remain narrowly authorized.
Documentation checked↗
Governance4 min read
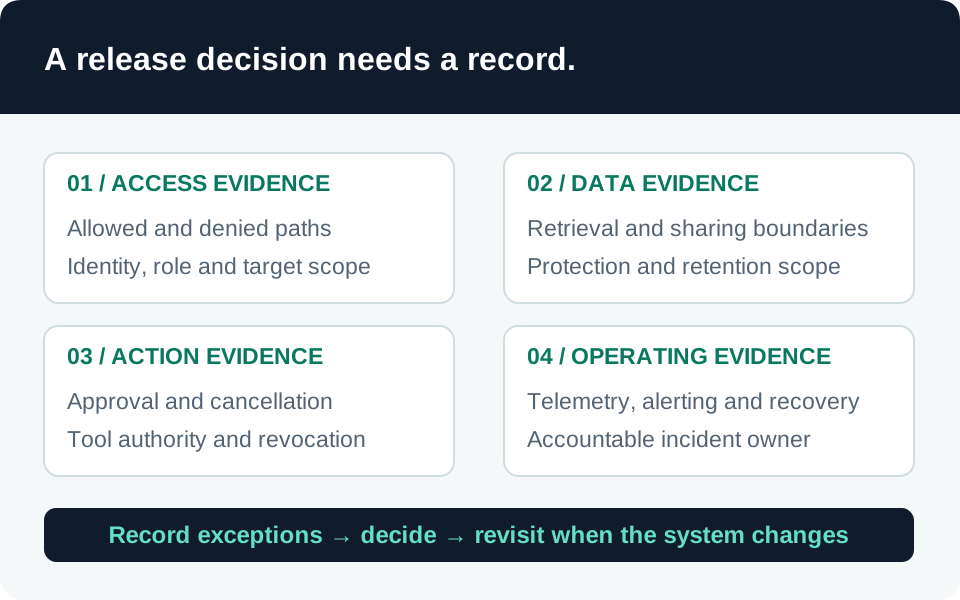
Tie each release to its identities, tools, data sources, test evidence, deployment settings, and recovery decision before expanding access.
Documentation checked↗
