Explore the topic

Conditional Access

Separate user, service-principal and managed-identity coverage; investigate policy outcomes without assuming universal enforcement.

2 guides4 queriesLatest review

Questions this collection helps you answer

  • Is this identity type in scope for the policy?
  • What do report-only, failure and not-applied results actually establish?

Build your understanding

Guides in this topic

All topics
Identity & authorization5 min read
Advanced guide

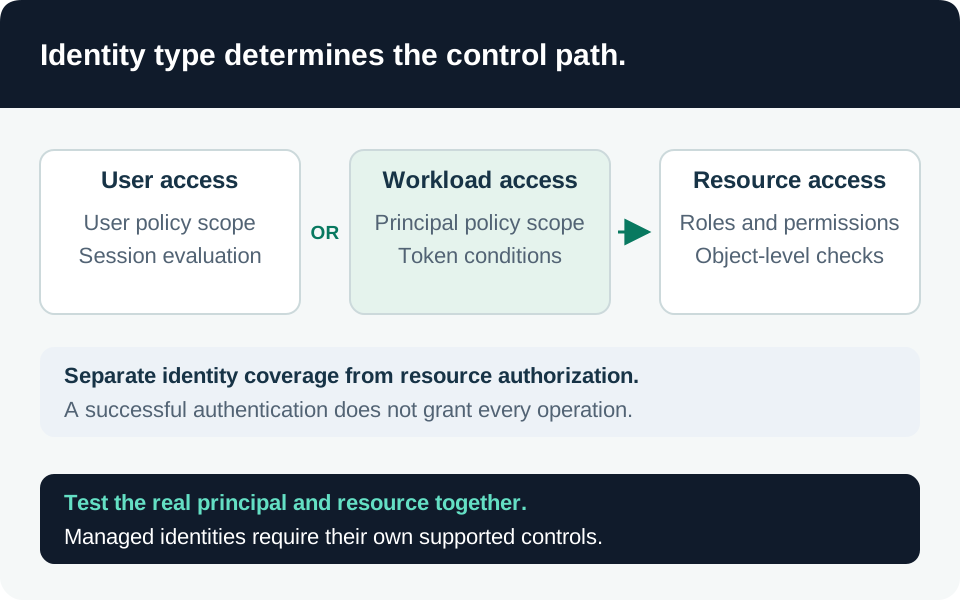
Design Conditional Access around AI identity types

Separate human, service-principal, managed-identity, and preview agent policy boundaries; validate token acquisition and resource enforcement independently.

Documentation checked
Identity & authorization7 min read
Advanced guide

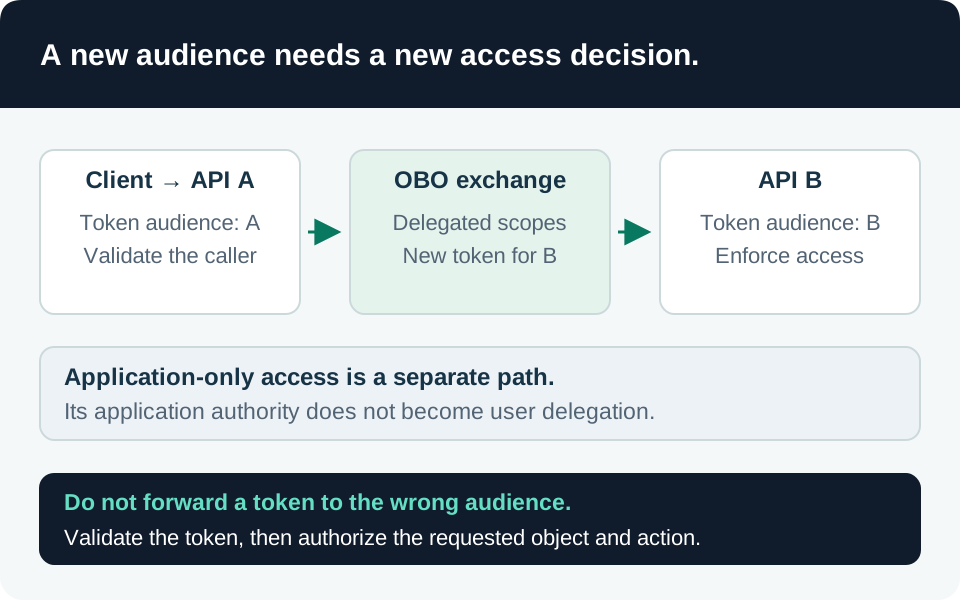
Design delegated authorization across an agent tool chain

Separate user delegation from application authority, validate token boundaries, and prevent an agent from turning an authorized session into an unauthorized action.

Documentation checked

Move from control to evidence

Related investigation queries

Use these as investigation leads. Table coverage and context determine what the results can establish.

All queries