Constrain privileged access across the AI control plane
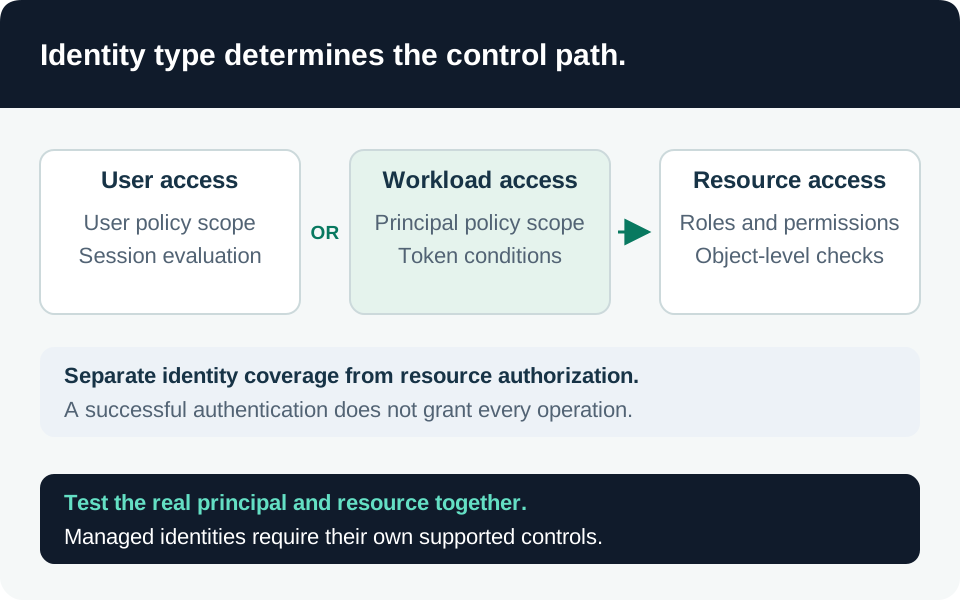
Design PIM activation, resource scope, approval evidence, and emergency recovery around the permissions that can change models, data, identities, and telemetry.
Explore the topic
Review temporary elevation, role assignment paths and recovery access around AI administration.
Questions this collection helps you answer
Build your understanding
Design PIM activation, resource scope, approval evidence, and emergency recovery around the permissions that can change models, data, identities, and telemetry.
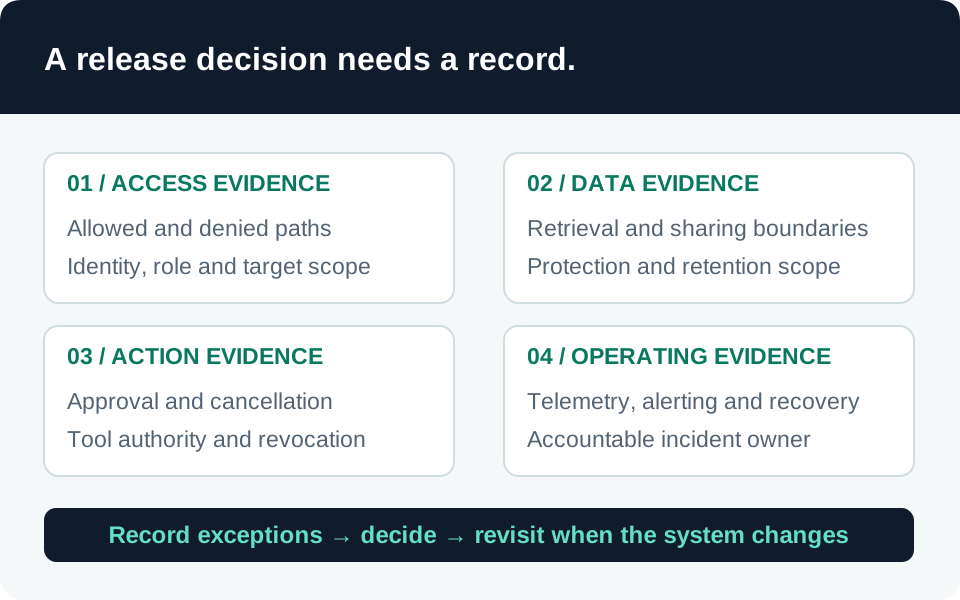
Tie each release to its identities, tools, data sources, test evidence, deployment settings, and recovery decision before expanding access.
Move from control to evidence
Use these as investigation leads. Table coverage and context determine what the results can establish.
Inspect recorded role-assignment writes and deletes, preserving operation status, caller and correlation evidence.
Anchor administrative activity to successful role-assignment changes by the same caller and subscription, without inferring activity by the grantee.
Count distinct successful membership audit events per actor and 15-minute window, preserving raw target samples for group and member resolution.
Separate direct, eligible, scoped and completed PIM role changes while retaining the full target payload for authoritative interpretation.
Follow the connections