Agents4 min read
Govern agent connectors before they move data
Turn a Copilot Studio connector inventory into scoped data policies, verified endpoint controls, and accountable changes across environments.
Documentation checked
Explore the topic
Investigate consent, owners, credentials and configuration changes that alter application authority.
Questions this collection helps you answer
Build your understanding
Turn a Copilot Studio connector inventory into scoped data policies, verified endpoint controls, and accountable changes across environments.
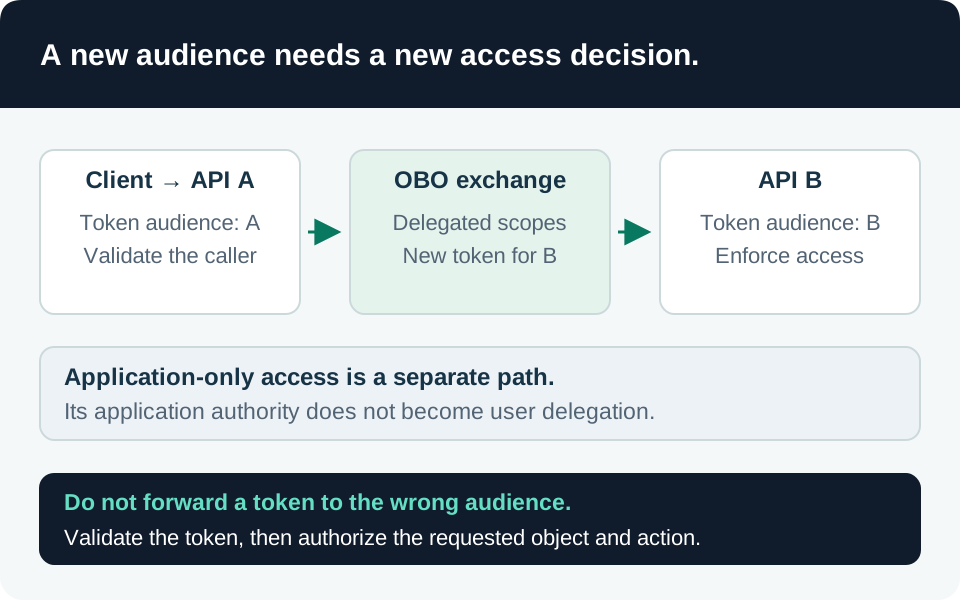
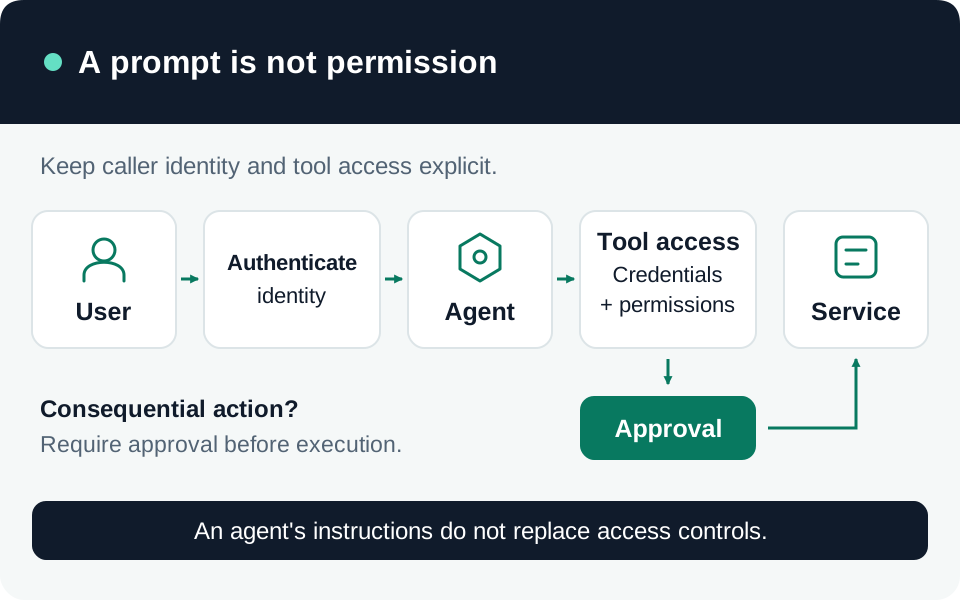
Separate user delegation from application authority, validate token boundaries, and prevent an agent from turning an authorized session into an unauthorized action.
Move from control to evidence
Use these as investigation leads. Table coverage and context determine what the results can establish.
Join credential additions to later successful sign-ins by directory and service-principal object ID without claiming the new credential was used.
Expand recorded application update properties and retain raw old/new values for review without assuming all fields have the same JSON shape.
Compare recent credential-management events with a separate seven-day actor/object baseline, retaining target type and change evidence.
Preserve initiator identity and every target's permission-change evidence for successful app-role, delegated-permission and consent events.
Inspect ownership additions and removals on application objects while preserving target relationships and distinguishing them from enterprise applications.
Track ownership changes on local service-principal objects without conflating them with the application's home registration.
Follow the connections