Collect AI security evidence without duplicating sensitive content
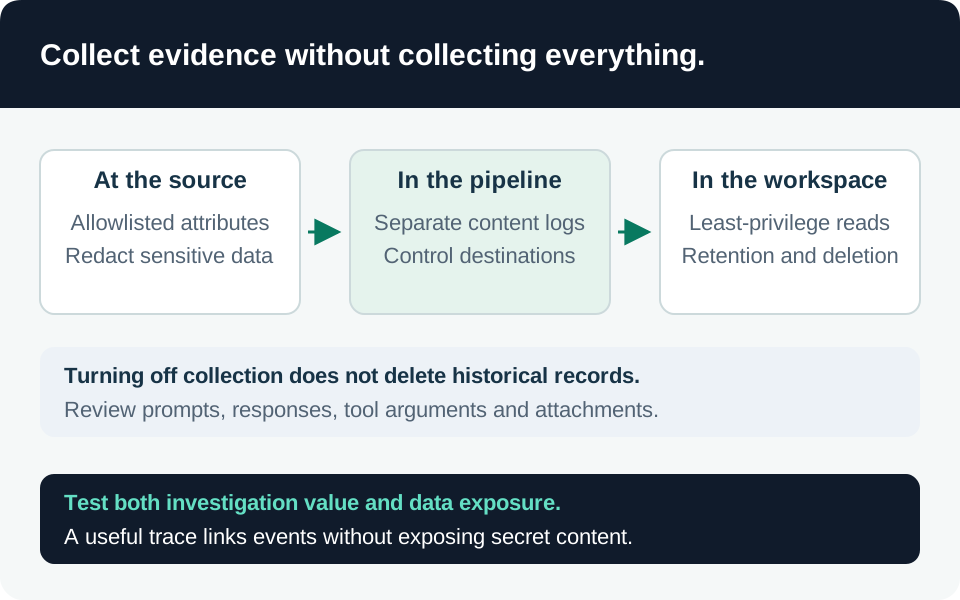
Design a telemetry contract that preserves authorization and action evidence, limits prompt capture, protects trace content, and tests leakage across logging paths.
Explore the topic
Verify source coverage and collection freshness while minimizing sensitive data in traces and investigations.
Questions this collection helps you answer
Build your understanding
Design a telemetry contract that preserves authorization and action evidence, limits prompt capture, protects trace content, and tests leakage across logging paths.
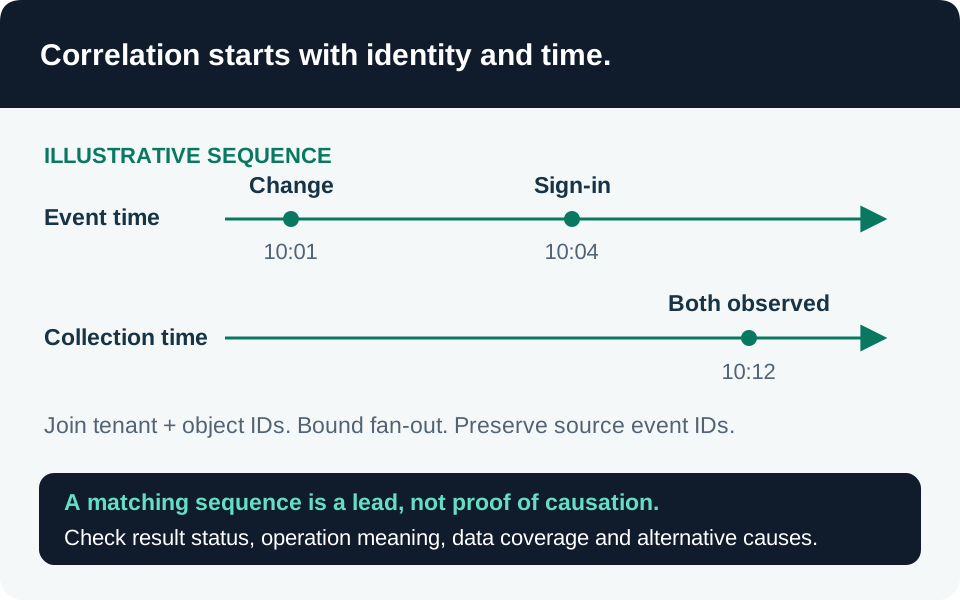
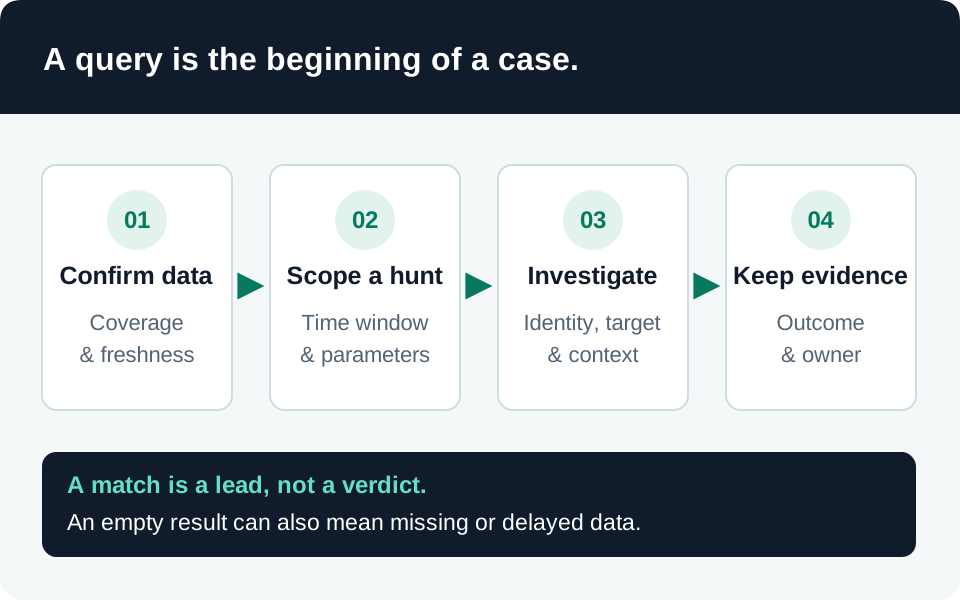
Test schema assumptions, event semantics, ingestion timing, join behavior, scheduling, entity mapping, and analyst outcomes before promoting a hunt into a detection.
Map Microsoft AI events to their real destinations, verify ingestion with controlled activity, and define evidence before writing detections.
Move from control to evidence
Use these as investigation leads. Table coverage and context determine what the results can establish.
Find recorded diagnostic-setting writes and deletions, retain operation outcomes, and investigate whether categories or destinations changed before declaring a logging gap.
Group failed interactive Entra sign-ins into 15-minute identity/IP windows for a bounded first-pass hunt.
Retain actor, target and changed-property evidence for successful authentication security-info updates without treating registration as account compromise.
Measure observed event-to-ingestion delay, timestamp gaps and empty sources across three security tables without treating missing data as healthy.
Find subscriptions and resource-log sources with sustained prior activity but no recent event-time rows, without treating quiet traffic as a proven ingestion outage.
Follow the connections