Explore the topic

Retrieval & data security

Protect document permissions, ingestion integrity and the storage behind AI grounding.

3 guides3 queriesLatest review

Questions this collection helps you answer

  • Do all retrieved chunks retain the correct permissions?
  • How are revocation, cache invalidation and index refresh verified?

Build your understanding

Guides in this topic

All topics
Retrieval & data security5 min read
Advanced guide

Secure the storage data plane behind AI retrieval

Separate ingestion and serving authority, close Shared Key and anonymous paths, constrain SAS use, and validate Blob and Data Lake access independently.

Documentation checked
Retrieval & data security7 min read
Advanced guide

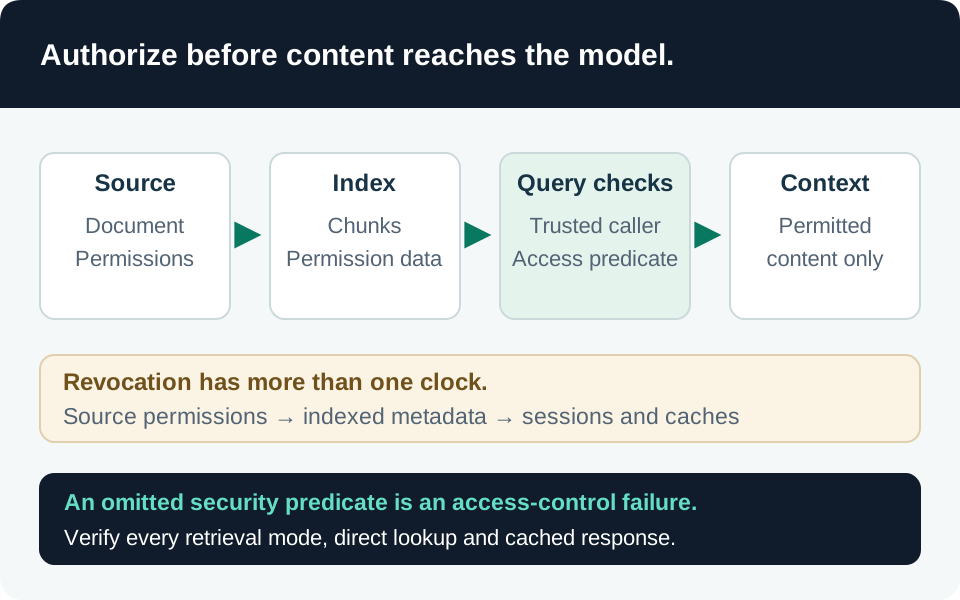
Enforce document authorization before RAG grounding

Choose between application security filters and native preview permissions, preserve access metadata on chunks, and enforce the same boundary across keyword and vector retrieval.

Documentation checked
Retrieval & data security7 min read
Advanced guide

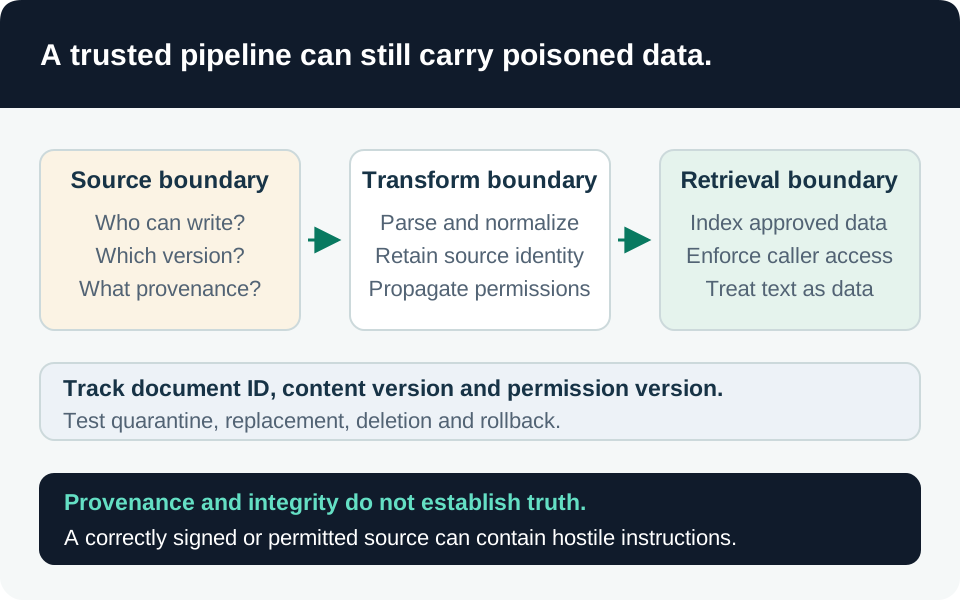
Protect RAG ingestion against poisoned and untraceable content

Separate source access from content trust, preserve provenance through chunking, and verify publication, deletion, and rollback without assuming a prompt filter proves integrity.

Documentation checked

Move from control to evidence

Related investigation queries

Use these as investigation leads. Table coverage and context determine what the results can establish.

All queries