Secure the storage data plane behind AI retrieval
Separate ingestion and serving authority, close Shared Key and anonymous paths, constrain SAS use, and validate Blob and Data Lake access independently.
Explore the topic
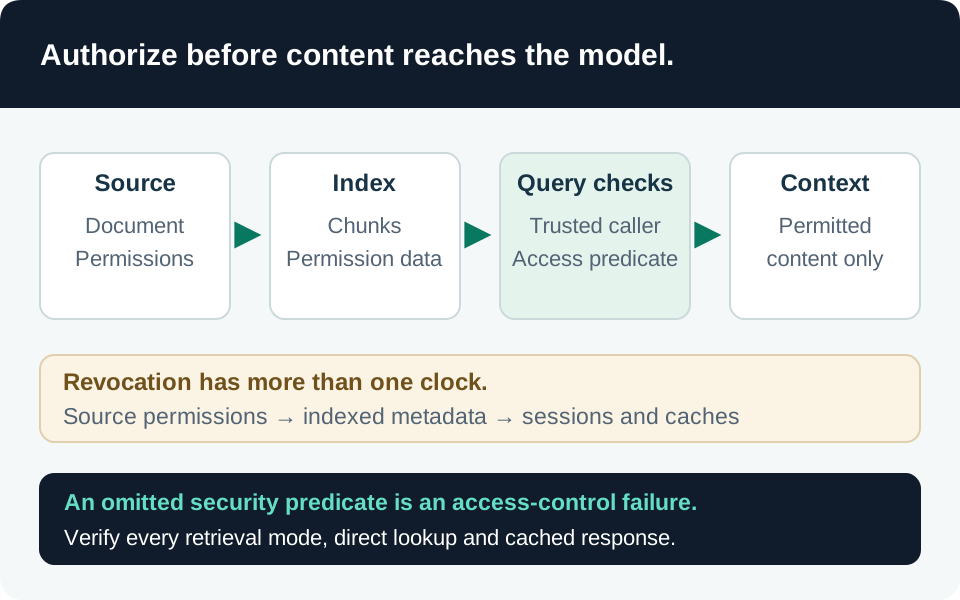
Keep tenant and document access checks intact through search, vector retrieval, grounding and caches.
Questions this collection helps you answer
Build your understanding
Separate ingestion and serving authority, close Shared Key and anonymous paths, constrain SAS use, and validate Blob and Data Lake access independently.
Choose between application security filters and native preview permissions, preserve access metadata on chunks, and enforce the same boundary across keyword and vector retrieval.
Move from control to evidence
Use these as investigation leads. Table coverage and context determine what the results can establish.
Quantify AccountKey-authenticated Blob requests by resource, client and operation category while retaining outcomes and transfer context.
Review SAS request outcomes and expiry-policy evidence without exposing token-bearing URLs or assuming all SAS access uses the same signing authority.
Follow the connections