Detection & response5 min read
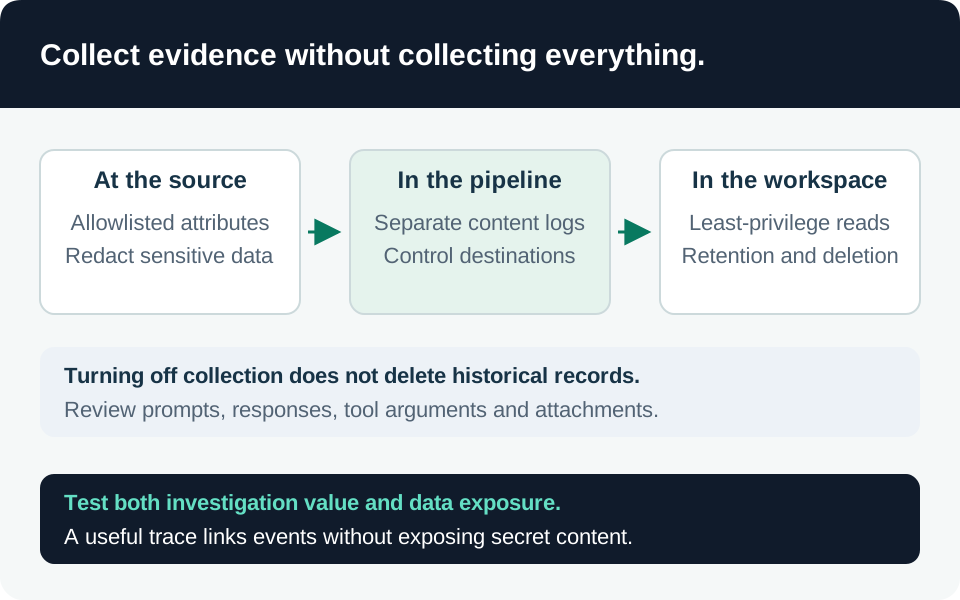
Advanced guideDesign a telemetry contract that preserves authorization and action evidence, limits prompt capture, protects trace content, and tests leakage across logging paths.
Documentation checked↗
Detection & response4 min read
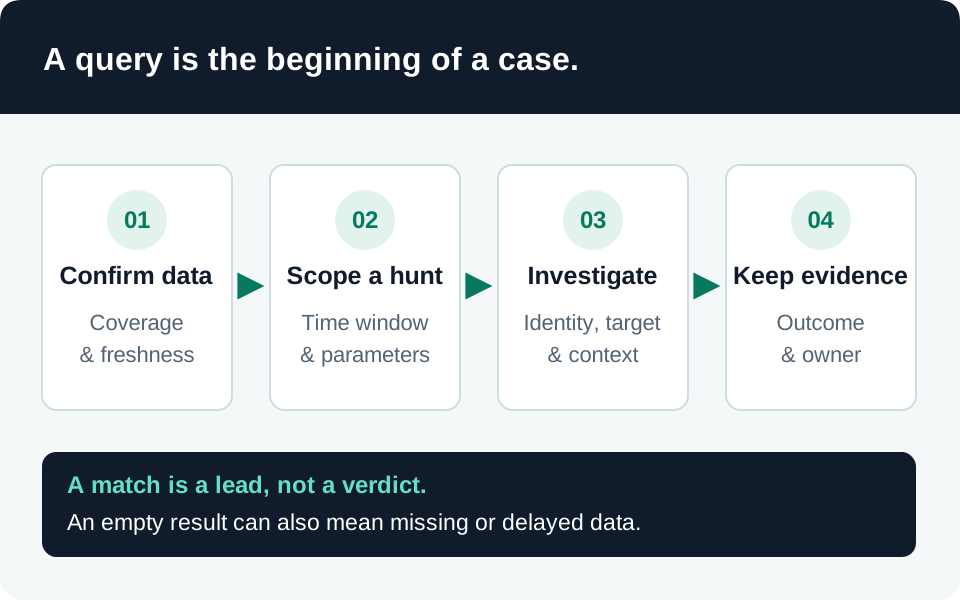
Preserve the native record, discover the actual Copilot schema, and build an evidence-backed timeline without confusing metadata with conversation content.
Documentation checked↗
Detection & response7 min read
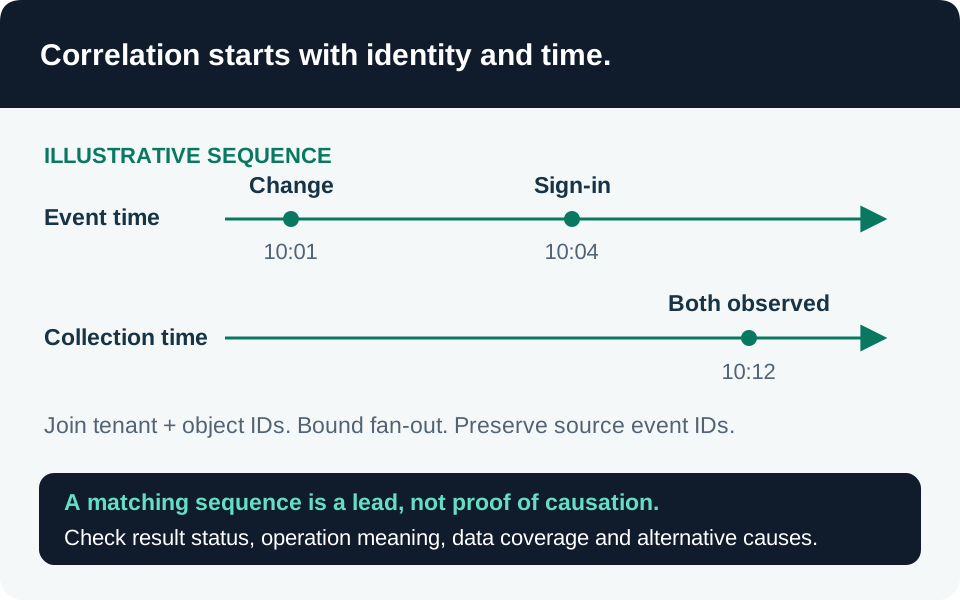
Advanced guideBuild defensible AI investigations with stable identity keys, explicit event grain, ingestion-aware scheduling, controlled joins and validated alert behavior.
Documentation checked↗
Detection & response5 min read
Advanced guideTest schema assumptions, event semantics, ingestion timing, join behavior, scheduling, entity mapping, and analyst outcomes before promoting a hunt into a detection.
Documentation checked↗
Detection & response4 min read
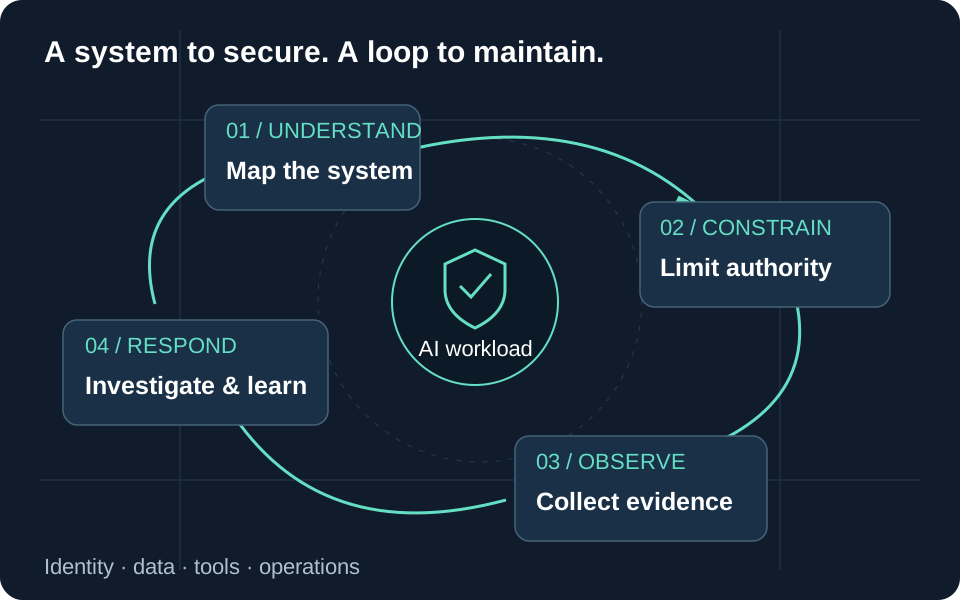
Turn a suspicious AI interaction into scoped containment, preserved evidence, a defensible impact assessment, and verified recovery.
Documentation checked↗
