Bind AI releases to verified artifacts and security evidence
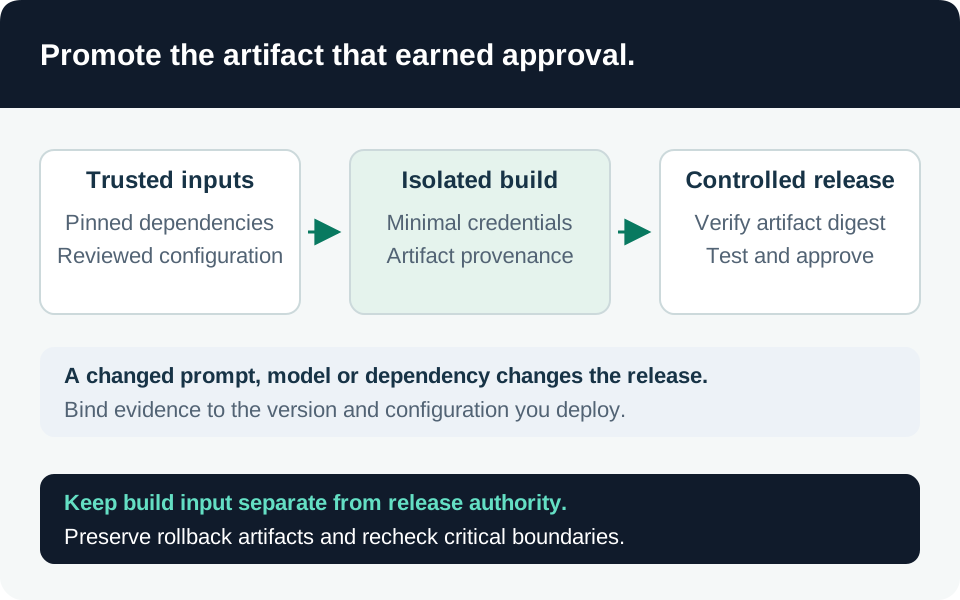
Version the model-facing release as a complete manifest, verify artifact identity and provenance, isolate deployment authority, and rehearse rollback without trusting mutable tags.
Explore the topic
Make release decisions with named owners, reproducible evidence and explicit exceptions.
Questions this collection helps you answer
Build your understanding
Version the model-facing release as a complete manifest, verify artifact identity and provenance, isolate deployment authority, and rehearse rollback without trusting mutable tags.
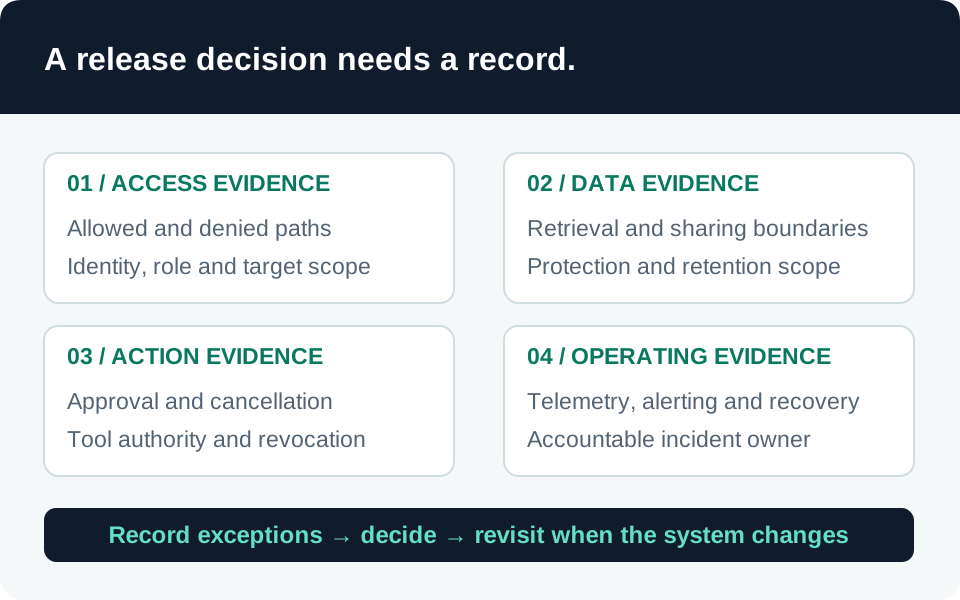
Tie each release to its identities, tools, data sources, test evidence, deployment settings, and recovery decision before expanding access.
Move from control to evidence
Use these as investigation leads. Table coverage and context determine what the results can establish.
Review successful lock mutations and identify the protected scope before assessing subsequent management changes or recovery risk.
Review successful assignment and exemption mutations with their resource scopes and initiating callers, then verify the effective policy outcome separately.
Inspect ownership additions and removals on application objects while preserving target relationships and distinguishing them from enterprise applications.
Follow the connections