Foundations4 min read
Build your Microsoft AI security baseline
Build an evidence-based baseline for Microsoft AI: identify the workload, constrain data and actions, test boundaries, and prepare incident response.
Documentation checked
Explore the topic
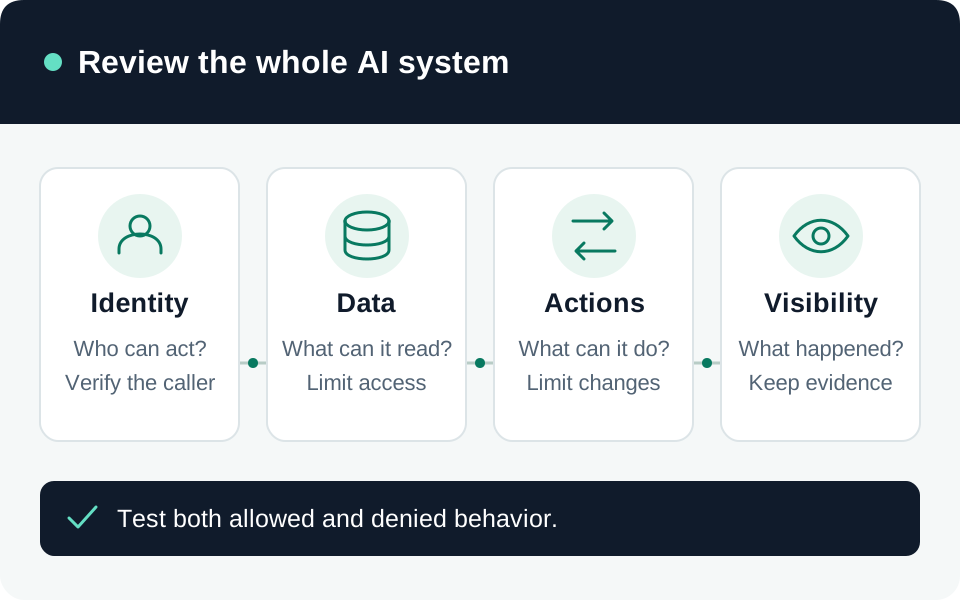
Map the system, establish the boundaries, and collect evidence that controls work.
Questions this collection helps you answer
Build your understanding
Build an evidence-based baseline for Microsoft AI: identify the workload, constrain data and actions, test boundaries, and prepare incident response.
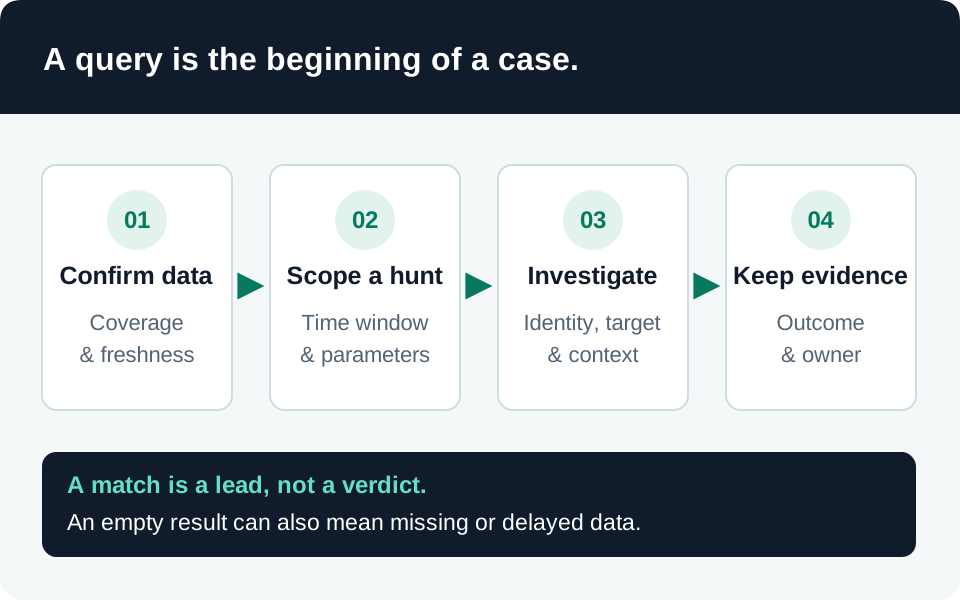
Map Microsoft AI events to their real destinations, verify ingestion with controlled activity, and define evidence before writing detections.
Move from control to evidence
Use these as investigation leads. Table coverage and context determine what the results can establish.
Measure observed event-to-ingestion delay, timestamp gaps and empty sources across three security tables without treating missing data as healthy.
Find subscriptions and resource-log sources with sustained prior activity but no recent event-time rows, without treating quiet traffic as a proven ingestion outage.
Follow the connections